Build useful AI governance for a team
A useful policy does more than approve or ban a tool. It connects real uses to risk, an accountable owner, expected evidence and a clear response when something fails.
The short answer
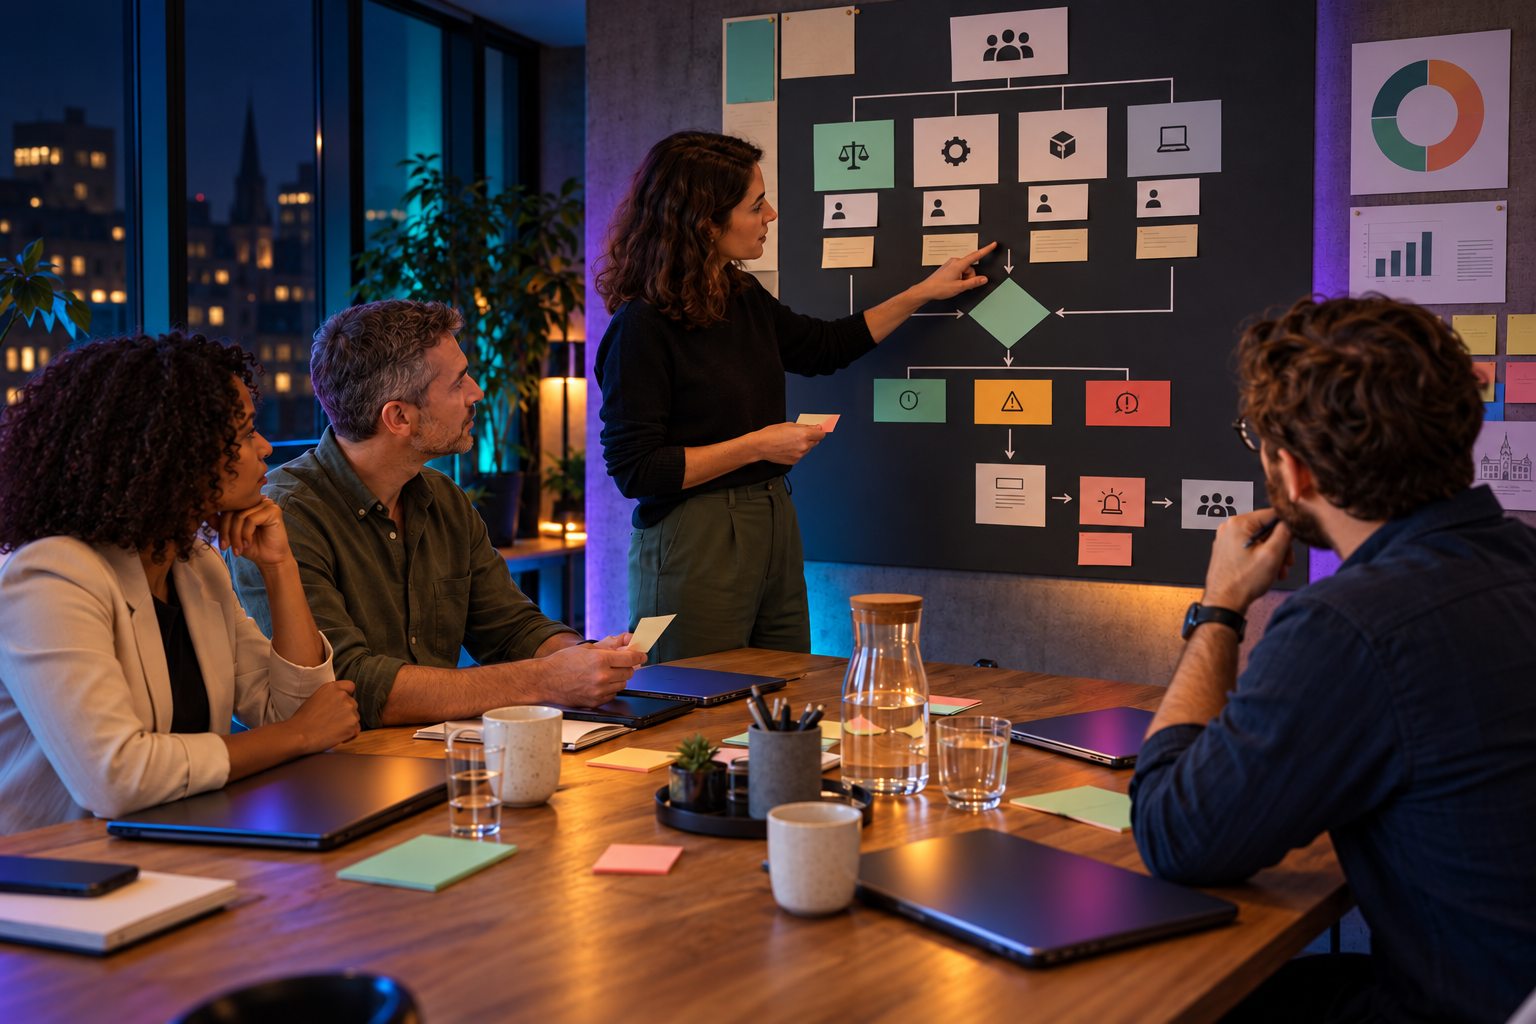
Inventory real uses, classify them by consequence, assign an owner and define proportionate controls. Centralise provider evidence, train with examples, then track incidents, exceptions and outcomes rather than licence counts.
- Govern real uses
- Name accountable owners
- Match controls to risk
Build a living framework

AI-generated illustration 1. Inventory uses
Record approved tools, individual experiments, extensions, APIs and automations. For each use, note data, audience, frequency, output and possible consequence.
Editorial illustration 2. Classify risk
Define a small number of levels based on data, autonomy, audience and impact. Link each level to actions that are allowed, prohibited or subject to approval.
Editorial illustration 3. Name the roles
Assign a business owner, technical contact, legal or security reviewer and monitoring owner. Shared responsibility without names leaves exceptions undecided.

AI-generated illustration 4. Qualify providers
Retain contracts, data processing terms, regions, subprocessors, security, export, deletion and review dates for each approved offer. Check the plan actually in use.
AI-generated illustration 5. Place approvals
Require competent review for public content and material decisions. Add approval before sending, publishing, paying, bulk changing or deleting.
AI-generated illustration 6. Learn from deviations
Provide a simple route to report error, leakage, bias, outage or unplanned use. Analyse causes, fix the workflow and update rules, training and tests.
Set triggers for a fresh review
Record the evaluated version, permitted data and system actions in the use-case register. For a document assistant, agree which checks to rerun when the model changes, a connector is added or permissions expand. The owner reviews the change against the original scope, records findings and decides whether it can go live.
Put the method to work

Practical case
Inventory AI tools used by one team for a single activity. Identify one permitted use, one uncertain use and one use to prohibit.

Evidence to keep
Record owner, transmitted data, provider, withdrawal path and who reviews an incident.

Make the decision
The rule is usable if the team knows what to do in all three cases without inventing an interpretation on the spot.
Four minimum registers

Uses
Who uses what, for which task, with which data and consequences?
Providers
Which plans, commitments, regions, durations and review dates?

Decisions
Who approved, on which evidence, with which limits and expiry?
Incidents
What happened, what impact, which correction and follow-up?
Platforms for equipping and orchestrating teams
Listing does not establish compliance. Examine the exact plan, administrative controls, integrations and your own obligations.

Zapier AI
task automation
Zapier · US
Visit official site
Make AI
task automation
Make · CZ
Visit official site
n8n
workflow building
n8n · DE
Visit official site
CrewAI
agent building
CrewAI · US
Visit official site
Langflow
workflow building
Langflow · US
Visit official site
Flowise
workflow building
Flowise · SG
Visit official siteHow is this selection produced?
These profiles are linked to the guide’s subject in our editorial catalogue. Inclusion is neither a ranking nor a performance measurement on your documents. Methodology.
Related tool families
Frequently asked questions
Is an AI committee required?
Not necessarily at first. Named owners, a short decision path and appropriate escalation for high-impact uses matter more.
How should individual experiments be handled?
Provide a sandbox without sensitive data, a short approved-tool list and a lightweight process for requesting a documented exception.
How often should governance be reviewed?
On a regular cycle and after incidents, offer changes, new connectors, scope extensions or relevant regulatory developments.
The references below expand on the concepts and checks discussed. Scenarios and trial frameworks remain editorial proposals; provider documentation describes its own product rather than an independent benchmark.
Source note
Organise AI governance in a small team
Inventory real AI uses before writing general rules: tools, entered data, output reviewers and affected decisions. Classify uses by their potential consequences for customers, the team and represented people.
Assign each use an owner and review it when the tool, data or context changes. Controls need observable evidence: trials, incidents, corrections and known limits.
Keep a short record per use: purpose, tool, permitted data, reviewer and stopping conditions. Start with existing practices, including unofficial projects. A rule becomes usable when someone can decide whether a document or task falls within scope.
Prepare reviews from actual examples: detected errors, corrections and results after changes. Offer a simple reporting channel without waiting for the next meeting. A model version or data-source change should trigger relevant retesting, not just a renamed register entry.
- Inventory
- List systems and the decisions they influence.
- Owner
- Identify who approves a use and handles incidents.
- Monitoring
- Record trials and reassess risks after changes.
Does every use require the same review?
No. Adapt checks to context and potential consequences while retaining an owner and decision record.
Fictional case — customer support
A team uses AI to draft responses, prohibits certain data entries, assigns approval to a support worker and records recurring errors to improve the process.
Try the reasoning
A small team appoints an AI owner but no deputy. Which situation should be tested?
Reasoning: Their absence during an error or stop request. Governance should specify who can suspend and resume the service.
Primary source : NIST — AI Risk Management Framework, Govern